
CMMC Level 2 overview
CMMC Level 2 protects CUI in nonfederal systems. The contract and current CMMC policy determine the required assessment and its timing.
Connect scope, safeguards, records, and proof
Section titled “Connect scope, safeguards, records, and proof”Readiness follows a clear chain. Each step depends on the one before it.
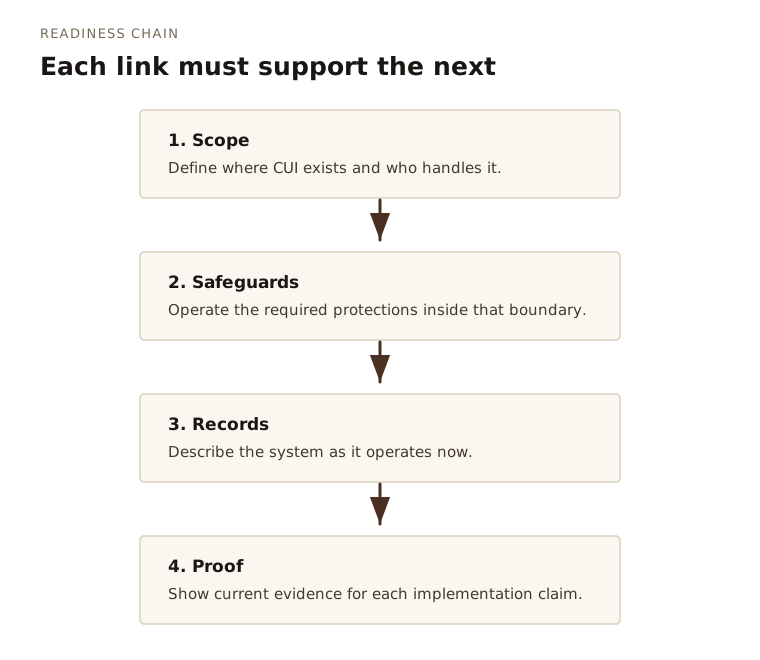
Start by defining where CUI exists and who handles it. Operate the required safeguards inside that boundary. Document how the system works. Then collect evidence that an assessor can use to verify each claim.
A missing link weakens the whole chain. A policy does not replace an operating safeguard. A safeguard without evidence is difficult to assess. Evidence from outside the documented boundary may not support the claim.
Working principles
Section titled “Working principles”- Follow the CUI. Map how CUI enters, moves through, and leaves the organization.
- Keep the scope defensible. Include everything the rules require, but avoid unnecessary expansion.
- Test every claim. Name the system, owner, frequency, and supporting evidence.
- Fix blockers first. Prioritize gaps by assessment effect, dependency, and operational risk.
- Write the SSP to match reality. Describe the system after the implementation is stable enough to document accurately.
- Keep people accountable. Qualified people must review contract interpretation, scope, architecture, scoring, and readiness decisions.
Published by Eagle Ridge Advisory. Public guidance only: this site holds no client information, completed security plans, evidence, or legal advice. Current CMMC rules and contract terms control.